> ## Documentation Index
> Fetch the complete documentation index at: https://docs.incident.io/llms.txt
> Use this file to discover all available pages before exploring further.
# Microsoft Intune on mobile
> Apply Intune app protection policies to the incident.io mobile app on managed and personal devices alike.
The incident.io mobile app supports Microsoft Intune Mobile Application Management (MAM), so your organization can enforce app protection policies on the incident.io app without requiring full device enrollment (MDM).
This lets you protect corporate data on both company-owned and personal (BYOD) devices by controlling actions like copy and paste, screenshots, and selective wipe, all scoped to the incident.io app.
Microsoft Intune on mobile is available on the Enterprise plan, and requires version 1.15.0 or later of the
incident.io app on iOS and Android.
## How it works
When Intune is enabled for your organization:
1. Users log into incident.io normally (SSO, email, etc.)
2. The app detects that your organization requires Intune and asks them to sign in with their Microsoft work account
3. incident.io checks that the account belongs to your linked Microsoft Entra tenant and matches their incident.io email
4. The app registers with Intune and your app protection policies are applied. Intune may restart the app the first time a policy applies.
After that, your policies are enforced inside the incident.io app, for example blocking screenshots or restricting data transfer, without managing the whole device.
incident.io links your organization to a single Entra tenant. That link is how we know which Microsoft accounts are yours, so connecting it is the first step in setup.
## Prerequisites
* The **Manage security settings** permission in incident.io
* A Microsoft Entra ID tenant with Intune licenses, plus admin access to the Microsoft Entra admin center and the Microsoft Intune admin center
* An app protection policy in Intune for iOS/iPadOS, Android, or both
* On Android, the Intune Company Portal app installed on each device. Intune requires it to apply app protection policies on Android.
* Everyone's incident.io email must match the email on their Microsoft work account
## Setting up Intune
Navigate to [Settings → Security](https://app.incident.io/~/settings/security) and find **Microsoft Intune on mobile**. Click **Connect Microsoft Entra**, confirm your company's email domain, then sign in with your Microsoft work account. incident.io links your organization to the tenant you signed in to.
For the link to succeed:
* Your Microsoft account email must match your incident.io email
* Your account must be a member of the tenant, not a guest
* The tenant must have verified the domain you entered
* The tenant can't already be linked to another incident.io organization
Connecting Microsoft Entra is one-way. Intune sign-ins and Microsoft Teams both depend on the linked tenant, so you can't remove or change it from the dashboard. Contact support if you need to.
If your organization uses incident.io with Microsoft Teams, your tenant is already linked and you can skip this step.
Still in [Settings → Security](https://app.incident.io/~/settings/security), enable **Microsoft Intune on mobile**.
Once enabled, incident.io activates the Intune enrollment gate in the mobile app. The next time each user logs in, they are asked to register the app with Intune before they can continue. People who are already signed in are not interrupted until then.
The incident.io mobile app uses a Microsoft Entra ID app registration to sign people in and to enroll with the Intune MAM service. A tenant admin needs to grant consent for it.
**incident.io app registration:**
* **Client ID:** `68ac5791-0672-47f9-a1e1-f2ef2b656f61`
* **App name:** incident.io
In the [Microsoft Entra admin center](https://entra.microsoft.com), go to **Identity → Applications → Enterprise applications**.
Search for the incident.io client ID: `68ac5791-0672-47f9-a1e1-f2ef2b656f61`.
If it doesn't appear, grant admin consent first (next step). Consenting is what adds the app to your tenant.
Open this URL in your browser, replacing `{TENANT_ID}` with your Entra tenant ID:
```text theme={null}
https://login.microsoftonline.com/{TENANT_ID}/adminconsent?client_id=68ac5791-0672-47f9-a1e1-f2ef2b656f61
```
Sign in as a Global Administrator or Application Administrator and accept the requested permissions.
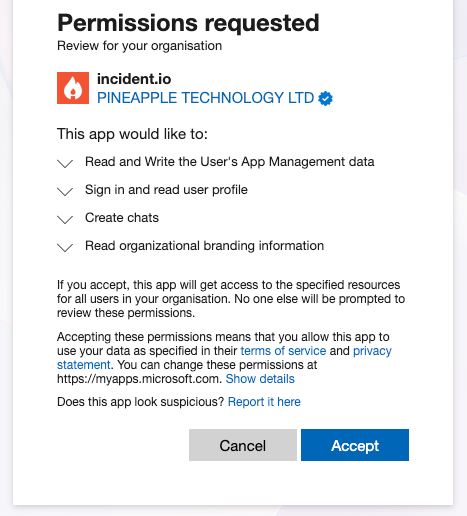 Back in **Enterprise applications → incident.io → Permissions**, check that both of these are granted:
* **Microsoft Graph:** `User.Read` (Sign in and read user profile)
* **Microsoft Mobile Application Management:** Read and Write the User's App Management data
Both should show a status of **Granted for \[your tenant]**. The consent screen also lists **Create chats** and **Read organizational branding information**. The same app registration powers the incident.io Microsoft Teams integration, which uses those.
Don't skip this step. Without admin consent for the Microsoft Mobile Application Management resource, the Intune SDK can't get the token it needs to enroll the app, and people see **Couldn't set up app protection** when they try to register.
In the Microsoft Intune admin center, go to **Apps → App protection policies** and open the policy you want to apply, or create one. Under **Apps**, add incident.io as a custom app:
| Platform | Bundle ID or package name |
| ---------- | --------------------------- |
| iOS/iPadOS | `com.incidentio.incidentio` |
| Android | `com.incidentio.incidentio` |
Under **Assignments**, include the groups whose members use incident.io. A policy applies only when both the app and the person are targeted.
In the policy's **Data protection** settings, keep **Org data notifications** set to **Allow**. incident.io pages
responders through push notifications, so don't block them.
Policy changes can take a few hours to reach devices. People can force a sync from the Company Portal app.
## Signing in on mobile
Here's what your team sees once Intune is on:
1. Sign in to the incident.io app as usual, with Slack, Microsoft, SAML, or an email code
2. The app shows **App protection required**. Tap **Continue with Microsoft** and sign in with the Microsoft work account that shares your incident.io email. If Microsoft Authenticator is installed, the sign-in goes through it.
3. The app registers with Intune. Intune may ask to restart the app the first time a policy applies.
On later launches the app opens straight to the home screen. Signing out deregisters the app from Intune and removes Intune-protected incident.io data from the device.
## What changes when Intune is on
* **Sign in on mobile via QR code** is unavailable.
* [Mobile access restrictions](/admin/mobile-access-restrictions) is replaced. Your Intune policies protect sensitive information instead of redaction, and the mobile app always signs in through your primary SAML connection.
* If you enforce [SAML SSO](/admin/saml-sso), it still applies. Intune adds a requirement rather than replacing one.
* Turning Intune on or off, and linking your Entra tenant, are recorded in [audit logs](/admin/audit-logs).
## Troubleshooting
Most problems show up when a responder taps **Continue with Microsoft**. Fix the cause, then have them tap **Try again**.
| What the responder sees | What to do |
| ----------------------------------------------------------------------------------------------- | -------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------- |
| **Couldn't set up app protection** with no other detail | The Microsoft sign-in or Intune registration failed. Check admin consent (step 3), the responder's Intune license, and their policy assignment, in that order. |
| `NOT_LICENSED`, or a message that the account isn't licensed | The account has no Intune license, or Intune couldn't reach its licensing service. Assign an Intune license in Microsoft Entra and wait a few minutes for it to apply. |
| `AUTHORIZATION_NEEDED`, or Microsoft's **Need admin approval** page | Your tenant hasn't consented to the **Microsoft Mobile Application Management** permission. Grant tenant-wide admin consent (step 3). |
| A message that the account is licensed but not targeted | No app protection policy applies to this responder. Add them to a group the policy is assigned to, and confirm the policy targets `com.incidentio.incidentio`. |
| `COMPANY_PORTAL_REQUIRED` | Android only. Intune needs the Company Portal app on the device to apply policies. Install Intune Company Portal from Google Play. No sign-in to it is needed. |
| **That Microsoft account has a different email from the one you signed in to incident.io with** | The account used for Intune is different from the one they signed in to incident.io with. Tap **Sign in again** and choose the member account with the matching email. |
| **Your sign-in expired while Microsoft Intune was setting up app protection** | Too much time passed between signing in to incident.io and finishing the Microsoft step. Tap **Sign in again** and complete the Microsoft step straight away. |
| Registration succeeded but policies aren't applying | The policy hasn't reached the device yet, or registration didn't complete. Wait for sync or force one from Company Portal. If the app isn't listed under **Apps → Monitor → App protection status**, sign out and back in. |
## FAQs
No. Intune on mobile uses app protection policies (MAM), so it works on personal devices as well as MDM-enrolled
ones. Full device enrollment through Company Portal isn't required.
No. Pages reach responders as push notifications, and SMS, phone call, Slack, and email escalations don't go through
the app at all. Keep **Org data notifications** set to **Allow** in your policy so pages always get through.
No. Intune on mobile is available in the incident.io app only. Read more about the [mobile app in
China](/on-call/china-mobile-app).
The basic profile of the responder signing in, which is enough to confirm their tenant and email match their
incident.io account. incident.io doesn't read your Intune policies or device inventory.